is investigating after users of its phone app received a notification claiming hackers had "fully compromised" the online fashion retailer's data.
The value of Asos's shares on the London stock exchange dived almost 12%, after thousands of customers received a mobile app notification titled "Asos hacked" which sent them to a message on the Telegram messaging service.
However, the website and app appeared to be continuing to operate on Tuesday morning and it is understood that Asos is still investigating whether any hack has taken place.
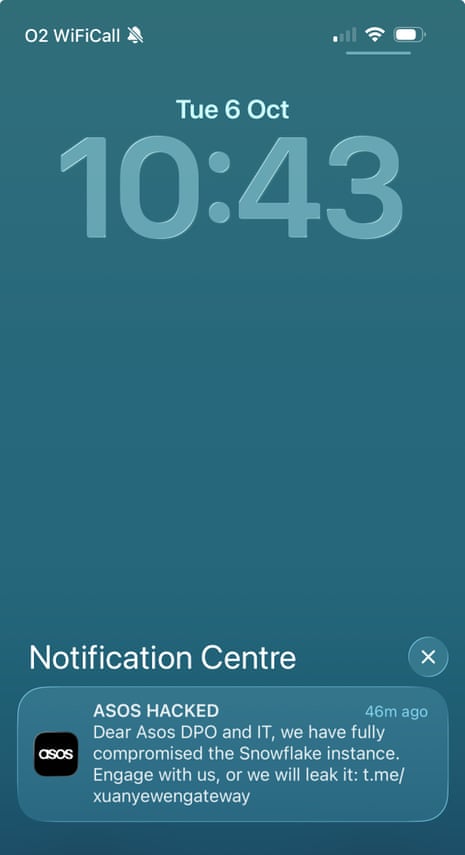
The message was sent out to customers said "Dear ASOS DPO [data protection officer] and IT, we have fully compromised the Snowflake instance."
Snowflake is a cloud platform used to store, process and analyse data collected by Simon AI including transactions and demographic information, such as clothing sizes and body measurements. It also enables push notifications to clients' phones.
, senior manager of security operations at , an online security firm, said:
Snowflake is a massive cloud database where retailers typically store sensitive customer information, a real worry if cyber criminals have indeed accessed it as they claim. The push notification suggests attackers have breached the systems controlling the ASOS mobile app also. This is clear public extortion.
Sending a ransom demand directly to consumer devices is an aggressive extortion tactic designed to force the business into a quick negotiation. I strongly advise shoppers to watch out for targeted phishing attempts while we wait for official confirmation of a data breach.
The potential hack comes after a string of British retailers including , the and suffered major hacking events last year. M&S and the Co-op experienced stock shortages and the former was forced to close its website for several weeks as it battled to ensure its systems were clean.
Germany's has initiated an "historic U-turn" by siding with and giving EU leaders effective permission to approve a "kill switch" to stop China further harming its economy, the country's leading financial newspaper has said.
Columnist in Handelsblatt says the new position would have been unthinkable three years ago yet has got "surprisingly little recognition" at home. He wrote today:
The German government initiated nothing less than an economic turning point on Monday. The coalition is realigning its China policy, putting an end to years of naiveté towards Beijing that cost German industry 15,000 industrial jobs every month.
Merz and Macron submitted proposals on Monday for new rapid-action measures to strike back against countries that harm it, including powers to cut off access to the EU single market if China or others that destablise trade relations.
The letter comes 10 days before EU leaders meet in Brussels to discuss safeguards to curb the now £1bn a day surplus in trade with China, reflected in soaring sales of everything from hybrid car sales to chemicals and components in manufacturing made in China.
They said "systemic market-distorting practices" jeopardise the bloc's economy and industrial base, requiring urgent action.
Their position paper is a remarkable U-turn for Germany given years of hostility to anything that would upset China, or the German car industry's investments in China.
Only two years ago the then German chancellor voted against tariffs on Chinese electric vehicle imports, siding with the German car industry.
But the mood in Germany has changed with to up 100,000 job losses predicted in and threats of cannibalisation to native industries.
On Friday the confederation of business industries, BDI, called for "derisking" while Eurometal, the EU-wide confederation of industries supplying metal components, has warned of widespread factory closures unless China is tackled.
Bank of England policymaker , who voted to raise interest rates in July and September, said that inflation has become embedded in the UK economy.
Inflation running above the Bank of England's 2% target risks getting further entrenched in wage negotiations early next year, she said today.
Last week, she said the Bank had erred in March, just after the start of the Iran war, by letting investors think it was happy to take a wait-and-see approach to raising rates.
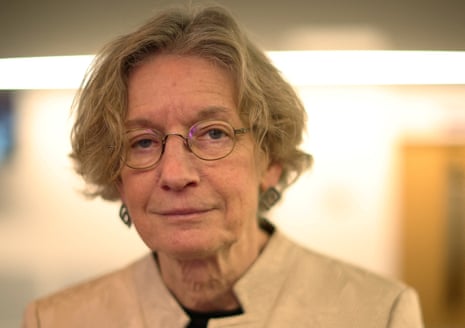
Mann, who joined the monetary policy committee (MPC) in 2021, said at a conference hosted by economic advisors TS Lombard:
We've had inflation well above target for the entire time that I've been in my position.... And so inflation has become embedded.
Unlike the European Central Bank and the US Federal Reserve, the Bank of England has kept interest rates unchanged since the outbreak of the Iran war. Traders now see an 80% chance of a rate hike at its November meeting, and a total of 100 basis points of rate rises by the end of next year. The Bank's base rate is at 3.75%.
Mann expressed concern that inflation looks set to hit 4% around the turn of the year, when many employers negotiate annual pay increases.
Other MPC members have said they will look for early signs of big wage increases, but have highlighted a weaker job market than when inflation last soared because of Russia's Ukraine war in 2022.
The central bank's governor is among a handful of policymakers speaking on Thursday.
The International Monetary Fund (IMF) has urged governments to respond to the latest energy price shock with targeted support for the poorest households, instead of by subsidising bills.
In a new blogpost, published ahead of the IMF's annual meetings next week, the Washington-based lender says energy price spikes can have long-lasting effects, and hit low-income households hardest.
By analysing the impact of the last energy crisis, in 2022-24, the IMF shows that, "for every euro spent suppressing electricity, natural gas, and gasoline prices, less than 20 cents reached the poorest fifth of households".
It also points out that by making energy cheaper for everyone, across-the-board subsidies, "weaken incentives to conserve scarce resources".
The IMF's analysis comes as the UK chancellor, , weighs up how much support to offer households in the UK ahead of an expected sharp rise in utility bills next January.
is set to appoint , the boss of the producer of shows including Destination X, as its new programming director and one of the most influential roles in British broadcasting.
Brindley, who will be responsible for the vast majority of the broadcaster's £640m annual programming budget, is effectively taking over from long-serving chief content officer who is departing this month.
Following an extensive recruitment process Brindley, who runs -backed production company Twofour, is understood to have won out over former Three and entertainment boss .
The appointment, which is expected to be announced imminently, marks the final shake-up of a new leadership team by new chief executive .
Last month, Dogra, the former Sky executive who took over from in March, unveiled the biggest round of layoffs in Channel 4's 43-year history as the financially challenged broadcaster seeks to dramatically cut costs.
Brindley will take on the title of director of programmes, after Dogra decided to split some of Katz's responsibilities between several executives.
While he will be responsible for the vast majority of unscripted and all scripted commissioning, , director of news, digital and audience trust, will head up current affairs and digital commissioning.
, director of content strategy, is the third member of Channel 4's senior commissioning leadership all of whom will report to Dogra.
Brindley previously worked for Channel 4 where he notched up credits including Educating Yorkshire, one of the channel's biggest hits, and joined Twofour as chief creative officer in 2020. He was appointed chief executive last year.
Channel 4 declined to comment.
Shares in the online fashion retailer Asos are down 13.3% now, after users of its mobile app received a notification claiming hackers had "fully compromised" the company's data. The company is investigating whether there has been a hack.
, ecommerce expert at the software company , said:
Asos's website never went down, but the commercial damage can start the moment customers lose trust in the messages coming through its own channels. People let a brand onto their phone because they trust it. Once that channel has been used to threaten them, they may start questioning genuine messages too.
Push notifications are one of the hardest-working channels retailers have. Across brands using Omnisend, push automations had a 22.9% conversion rate last year. If customers now switch notifications off or stop engaging with them, that could have a direct impact on repeat sales.
The first practical step is to pause any automated promotional sends. A discount arriving before an explanation of that notification risks making customers feel their concerns are being ignored.
With Black Friday approaching, Asos will want existing customers to feel comfortable buying again. If shoppers disengage from push notifications and email now, that is revenue the brand may find difficult to win back.
Here's more reaction.
lead security researcher at the anti-virus provider , said:
The ability of hackers to directly contact potential victims through push notifications in the Asos app highlights how disruptive cyber incidents can be when threat actors gain access to trusted communication channels. Beyond the immediate technical impact, incidents like this can quickly undermine customer trust, particularly when alarming messages appear to come from a legitimate organisation.
While attackers have reportedly claimed to have compromised a Snowflake environment, organisations should avoid drawing conclusions based solely on statements made by cybercriminals. Establishing what systems were accessed, what data may have been exposed, and how attackers gained entry requires a thorough forensic investigation.
Regardless of the attack path, the incident reinforces the importance of strong identity and access management across cloud environments. Recent investigations by Kaspersky have shown that cybercriminals increasingly rely on misconfigurations, exposed services and legitimate tools already present within an organisation's environment rather than sophisticated malware. In some cases, attackers have even abused trusted business systems, including corporate printers, to deliver ransom demands directly to employees and amplify the psychological impact of an attack.
She added that customers whose data may have been compromised should remain alert to follow-on phishing and social engineering attempts. Cybercriminals often exploit the confusion surrounding high-profile incidents, using convincing messages that appear to come from trusted organisations.
Here's our full story on , and a bit of a potted history below.
, which stores data for many major companies including Asos, has reportedly been the target of a number of data breaches in recent years, including an attack on which saw customer details stolen.
London-headquartered Asos, which owns brands including and , has 17 million customers around the world, in more than 150 countries. It employs 2,800 people.
The UK is its group's largest market, accounting for nearly half (49%) of revenues in its first half results.
The fast fashion retailer was founded in 2000 under the name As Seen on Screen, and became popular for its fashion and accessories sported by celebrities in films and on TV. It grew from a tiny startup into the UK's largest online fashion and beauty retailer by 2014. Its chequered red-and-white skater dress, was worn by Michelle Obama, and it later saw explosive growth during Covid lockdowns.
However, more recently Asos has struggled against competition from , and others, and is in the middle of a major turnaround programme as it tries to reverse a drop in sales and return to profit.
Asos has turned to online stylists powered by artificial intelligence as it attempts to win back customers.
Late last year, the company said it was testing "Styled for You", which uses AI trained on its database of 100,000 curated outfits to suggest items that could go together with those a shopper has already bought or has searched.
, vice president of market strategy at the automated cyber investigation platform , said:
This notification was psychological warfare, designed to whip up panic. Attackers know that any panic piles on the pressure on Asos to think about paying up rather than taking time to develop a rational response.
This is a clear shift in how we see breaches: from learning after the fact, to thousands of users seeing the news pushed onto their phone home screens in real time.
The next few hours are crucial. Asos cannot let panicked pressure dictate its response. The priority must be investigation, and closing the gap that allowed this mass notification to go out. Activity like this will surely have huge noise around it that leaves a clear trail, so there should be plenty of evidence of what happened and how to fix it.
This is also further evidence of the pressure security teams are under. They are overloaded: 15% of security alerts have to be flat-out ignored, 37% of vulnerabilities go undiscovered, and the focus is so totally on alerts and response that teams cannot proactively hunt threats before they strike. In this environment something will inevitably break through.
, chief technology officer at part of the cybersecurity software company , said:
This is an unusually brazen and threatening message. The attackers aren't simply claiming to have breached Asos - they're publicly telling the company to engage with them or they will leak what they say they have obtained.
What makes it even more concerning is how that threat appears to have been delivered. A message apparently written for ASOS's data protection and IT teams has instead been pushed directly to customers through the company's own app notification system. That suggests someone has gained unauthorised access to at least part of Asos's systems, although we don't yet know how extensive that access is.
The attackers claim they have 'fully compromised' Asos Snowflake instance. Snowflake is a cloud data platform businesses use to store and analyse large quantities of information. If that claim proves genuine, the critical question will be what information was held there and whether any of it was accessed or downloaded. At this stage, however, customers shouldn't assume their personal or payment information has been stolen - that hasn't been established.
What customers should be particularly alert to now is what happens next, Briedis said.
High-profile cyber incidents create ideal conditions for phishing attacks. Criminals may exploit the publicity by sending emails and texts claiming to be from Asos, perhaps asking customers to reset a password, confirm payment details, check an order or claim a refund.
Don't click links in unexpected messages, even if they look convincing. Go directly to the Asos app or website instead. Customers should also make sure their Asos password is unique and, if they've used the same password elsewhere, change it on those accounts too.
Until Asos completes its investigation, we won't know exactly what has been accessed or how the attackers got in. But this incident shows how powerful access to a trusted communications channel can be. When an attacker can potentially speak to customers through a company's own systems, it makes the threat considerably more convincing and potentially much more damaging.
is investigating after users of its phone app received a notification claiming hackers had "fully compromised" the online fashion retailer's data.
The value of Asos's shares on the London stock exchange dived almost 12%, after thousands of customers received a mobile app notification titled "Asos hacked" which sent them to a message on the Telegram messaging service.
However, the website and app appeared to be continuing to operate on Tuesday morning and it is understood that Asos is still investigating whether any hack has taken place.
The message was sent out to customers said "Dear ASOS DPO [data protection officer] and IT, we have fully compromised the Snowflake instance."
Snowflake is a cloud platform used to store, process and analyse data collected by Simon AI including transactions and demographic information, such as clothing sizes and body measurements. It also enables push notifications to clients' phones.
, senior manager of security operations at , an online security firm, said:
Snowflake is a massive cloud database where retailers typically store sensitive customer information, a real worry if cyber criminals have indeed accessed it as they claim. The push notification suggests attackers have breached the systems controlling the ASOS mobile app also. This is clear public extortion.
Sending a ransom demand directly to consumer devices is an aggressive extortion tactic designed to force the business into a quick negotiation. I strongly advise shoppers to watch out for targeted phishing attempts while we wait for official confirmation of a data breach.
The potential hack comes after a string of British retailers including , the and suffered major hacking events last year. M&S and the Co-op experienced stock shortages and the former was forced to close its website for several weeks as it battled to ensure its systems were clean.
customers have been sent a phone alert saying the retailer has been hacked, and the online fashion retailer is investigating.
Customers received a mobile app notification on Tuesday, titled "Asos hacked", which directed them to a Telegram account.
The message read: "Dear ASOS DPO [data protection officer] and IT, we have full compromised the Snowflake instance. Engage with us, or we will leak it," followed by the Telegram link.
Shares in the company tumbled almost 12%, making them the biggest faller on the FTSE 250 index.
It comes after a raft of UK retailers have been targeted by cyber attackers over the past two years, including , the and – as well as carmaker .
Europe needs to double its use of electricity by 2040 to reduce emissions but to also provide critical shock absorbers for gas and oil price spikes, Ursula von der Leyen has said, reports Lisa O'Carroll from Brussels.
The price of gas had soared 140% since the US-Israeli assault on Iran began on 28 February, while diesel has doubled in price, the European Commission president told parliamentarians in Strasbourg.
In total the EU has paid more than €100bn extra for fuel "without a single molecule extra of energy" being imported or produced. Von der Leyen said:
Today, electricity accounts for less than a quarter of our final energy consumption. Therefore, our Electrification Action Plan sets clear targets to double that by 2040.
Measures across the bloc were different according to need with France and Romania offering vouchers for the low-income households. It would also be prolonging state-aid energy focussed programme for industries, Accelerate EU, she announced as well as participating in the release of 100m barrels of oil, announced by the G7 last Friday.
Construction activity across the UK remained in decline last month, but the downturn was the least pronounced since the start of the year, according to a closely-watched survey.
The purchasing managers' index for construction from S&P Global rose to an eight-month high of 46.1 in September from 44.3 in August, but remained well below the 50 mark that separates growth from contraction. It has been in decline since January last year.
A sharp downturn in housebuilding eased slightly but it remained the weakest area, followed by civil engineering, while commercial work showed only a small decline.
, economics director at S&P Global Market Intelligence, said:
The downturn in UK construction output was the least marked since January. All three sub-sectors have seen a degree of stabilisation relative to the rapid declines reported in the second quarter of 2026. In September, commercial building work saw its smallest fall in activity since May 2025. House building was again the weakest performer as rising borrowing costs and unfavourable market conditions weighed on output.
Total new orders were relatively subdued in September as construction firms reported longer sales conversion cycles and clients deferred decision-making on major projects.
The new orders measure fell to a three-month low of 45.9 from 47.7, amid subdued demand, geopolitical tensions and rising input costs.
Companies' costs rose at their slowest rate since the outbreak of the Iran war in late February, but Moore said this was unlikely to last due to higher energy and transport costs.
Business optimism was the weakest since May.
S&P Global said its all-sector PMI survey, which includes data for services, manufacturing and construction, slipped to a three-month low of 51.5 in September from 51.8.